
Security monitoring & triage
Review meaningful security signals, investigate suspicious activity, assess severity, and provide clear, actionable findings.
Managed SOC services built around your organization and the security tools you already have. We help connect the evidence, prioritize the real threats, and guide the response.
Practical expertise for organizations that need capable security monitoring and investigations without buying and operating another entire tool stack.
Review meaningful security signals, investigate suspicious activity, assess severity, and provide clear, actionable findings.
Build event timelines, correlate available evidence, identify affected entities, and support containment and escalation.
Improve alert quality with refined rules, detection logic, coverage reviews, and tuning to reduce unnecessary noise.
Identify gaps in logging, identity protections, endpoint coverage, and security operations workflows.
Get readable investigation summaries, prioritized findings, and recommended next steps grounded in available telemetry.
Build escalation paths, improve playbooks, and establish practical procedures before an incident occurs.
We aim to work with the security platforms and licenses you already use. Any gaps or optional additions are discussed, not imposed.
A developing security investigation workbench designed to help analysts turn scattered logs and alerts into organized evidence, defensible findings, and the next useful action.
Explore real screenshots from a tested development build using synthetic case data. Phantom is not yet a publicly released product.
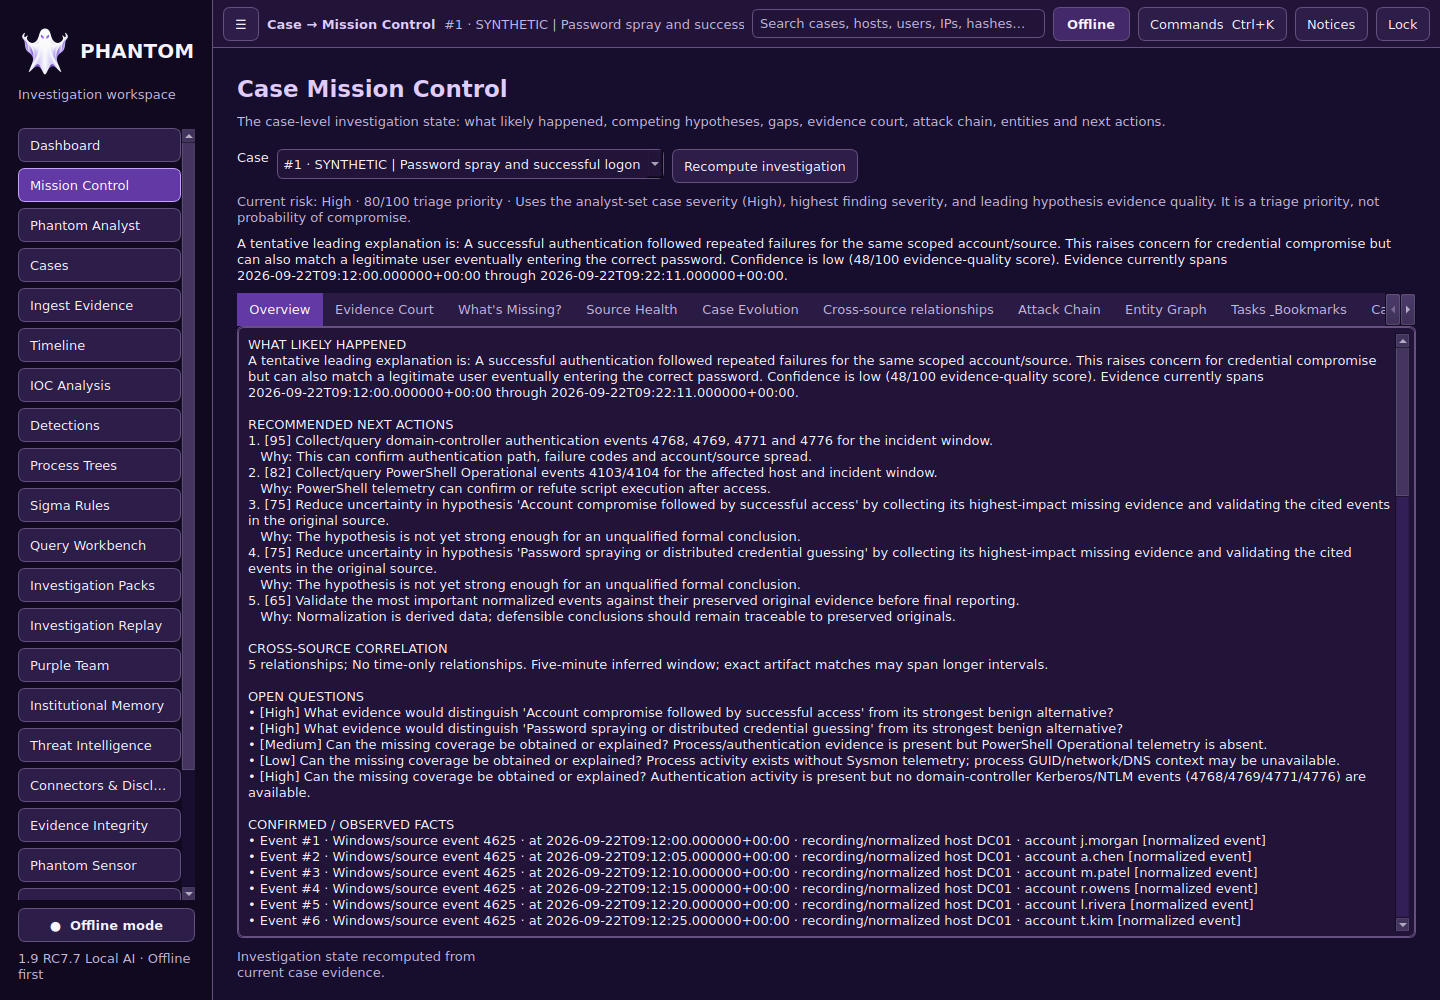 Actual development-build capture · Synthetic case data
We focus on what happened, what the evidence supports, and what your team should do next.
Map key assets, existing platforms, available telemetry, business risk, and escalation requirements.
Work from your identity, endpoint, email, firewall, and SIEM data wherever supported by your environment.
Validate suspicious behavior, preserve context, and distinguish confirmed findings from leads.
Deliver concise reporting and response guidance aligned to your agreed service scope.
Many organizations already have valuable security capabilities they are not using to their full potential. Phantom is designed to complement your tools, workflows, and licenses—not force a replacement.
Specific platforms, access methods, response authority, and monitoring hours are confirmed during scoping. No affiliation with third-party vendors is implied.
Tell us what you're trying to protect and how your current operations work. We'll discuss what a practical engagement could look like.
Whether you need a more capable SOC process, investigation support, or better visibility from existing tools, we can discuss a right-sized scope.
Please do not submit passwords, log extracts, personal records, incident details, or other sensitive information here.